
Indonesia runs on mobile. Payments, ride-hailing, e-commerce, and government services have all moved online faster than in almost any other Southeast Asian market. That speed taught a hard lesson: connectivity without resilience is a liability. Today, Indonesia’s cybersecurity is moving from a compliance checkbox to a board-level operating discipline. Regulators, CISOs, and vendors are rewriting the playbook around a different question. It is no longer “can we stop every breach?” but “how fast can we withstand, contain, and recover?”
The Wake-Up Call That Reframed the Conversation
The turning point was the ransomware attack on the National Data Center (PDN), which contributed to a decline in Indonesia’s Global Cybersecurity Index ranking, reported as 84th. Beyond the headlines, the incident exposed a familiar architectural weakness: concentration risk. When many agencies’ workloads depend on one infrastructure with weak backup segregation, a single compromise cascades across services.
The lessons were technical and immediate. Organizations began rethinking immutable and offline backups, tested recovery objectives (RTO/RPO), network segmentation, and the difference between having a disaster recovery plan and having one that actually works under pressure.
Regulation Is Catching Up
Policy has been moving in parallel. The Personal Data Protection (PDP) Law requires controllers to notify affected data subjects and the data protection authority within 72 hours of a failure to protect personal data. On the operational side, BSSN Regulations 1/2024 and 2/2024 cover cyber incident management and cyber crisis management, giving organizations a clearer basis for reporting and response.
The bigger piece is still pending. The Cybersecurity and Cyber Resilience Bill designates BSSN as the central authority, reporting directly to the President, and it appears on the 2026 priority list, aiming to replace a patchwork of regulations with a unified framework. It hasn’t been without debate, as commentators have raised concerns about the proposed military role and civil-liberties risks. Either way, the direction is clear: from fragmented, sector-specific rules toward coordinated national oversight.
A Threat Landscape That Doesn’t Blink
The scale is striking. BSSN recorded roughly 5.5 billion cyberattacks in 2025, with the trend continuing into 2026 and the majority malware-driven. But raw volume is a noisy metric. The real risk sits in the quieter, targeted activity: ransomware operators, credential theft, business email compromise, and increasingly personalized, multi-channel social engineering that bypasses technical controls by going after people.
From Perimeter to Resilience: What’s Changing Technically
This is where Indonesia’s cybersecurity maturity shows most clearly. The shift isn’t about buying more tools. It’s about architecture and operating model.
- Identity-first security: Zero trust principles, MFA everywhere, privileged access management (PAM), and identity threat detection are replacing the old castle-and-moat model. If credentials are the new perimeter, they need the strongest controls.
- Detection and response: Organizations are investing in EDR/XDR, SIEM correlation, and 24/7 SOC or MDR coverage. The metrics that matter are mean time to detect (MTTD) and mean time to respond (MTTR).
- Recoverability by design: Immutable backups, isolated recovery environments, and regular restoration drills are becoming standard for critical systems.
- Cloud and data governance: With workloads moving to the cloud and local data centres expanding, data residency, cross-border transfer rules, and shared-responsibility clarity now sit on the boardroom agenda.
- Third-party and supply chain risk: Vendor access, API exposure, and SaaS sprawl are treated as attack surface, not procurement footnotes.
- Rehearsed incident response: Tabletop exercises, defined playbooks, and coordination with sector CSIRTs are replacing improvisation.
AI Cuts Both Ways
Attackers use AI to scale phishing, clone voices, and speed up reconnaissance. Defenders use it to correlate signals across identity, endpoint, network, and cloud, and to cut analyst fatigue. AI-assisted development is also raising a new question: when teams can generate code far faster, who verifies what that code can access and expose? Secure-by-design practices and governance over AI use are quickly becoming part of the resilience conversation.
The People Layer
Technology alone can’t close the gap. Skills shortages, alert fatigue, and inconsistent security awareness remain persistent constraints. The organizations progressing fastest pair technical investment with role-based training, phishing simulation, clear escalation paths, and executive ownership of cyber risk. In other words, they treat resilience as a people, process, and technology problem.
Where the Ecosystem Converges
- Cybersecurity progress depends on meaningful collaboration between public institutions, private organisations, and security professionals.
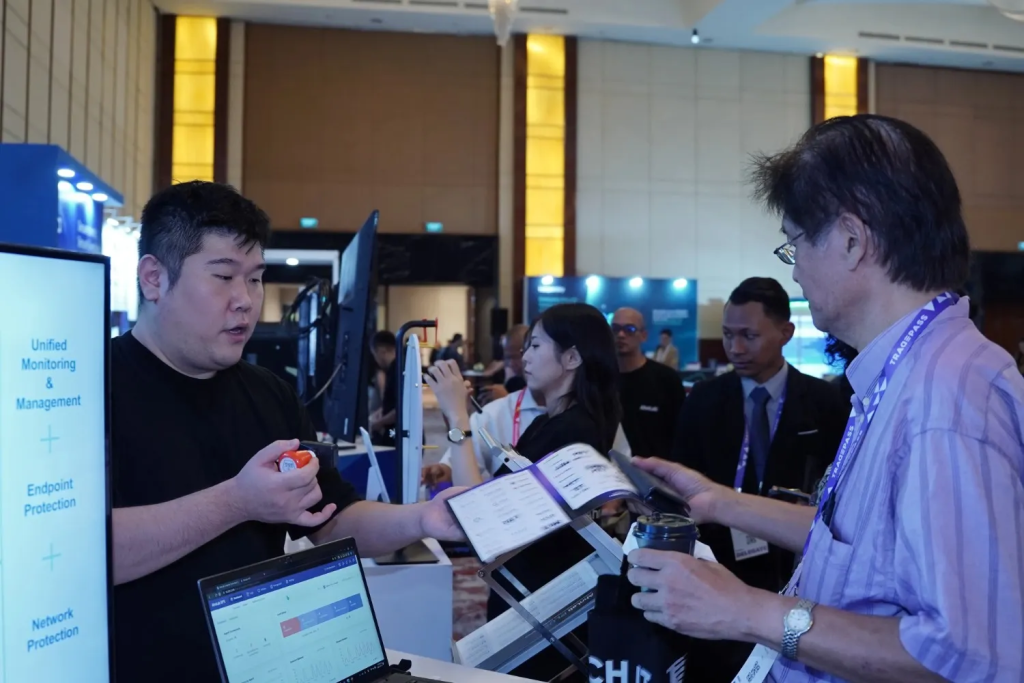
- The 9th edition of the IndoSec Summit in Jakarta brought these groups together to exchange practical knowledge and discuss evolving cyber risks.
- Speakers from BSSN and KOMDIGI shared perspectives alongside CISOs representing the banking, fintech, and telecommunications sectors.
- Key discussions covered zero-trust security, cloud protection, digital forensics, IoT risks, and cyber warfare, reflecting the increasingly complex threat landscape.
- A closed-door CISO Lounge provided space for senior security leaders to discuss challenges and experiences more openly with their peers.
- The combination of policy guidance, practitioner insights, and technology demonstrations helped connect strategic cybersecurity priorities with real-world implementation.
- Such industry gatherings can help organisations better understand regulatory expectations while exploring practical approaches to strengthening digital resilience.
Conclusion
Indonesia’s cybersecurity shift is less about a single reform and more about a change in mindset: assume compromise, design for recovery, and share intelligence across sectors. Regulation is tightening, architectures are modernizing, and leaders are treating cyber risk as business risk. Staying current means engaging with peers, regulators, and practitioners, and well-run events in cyber security remain one of the fastest ways to do that. The organizations that build resilience now will be the ones that keep trust when the next incident arrives.
IndoSec, organized by Tradepass, is Indonesia’s flagship cybersecurity summit, championing secure digital growth since 2018. Its 9th edition in Jakarta, supported by BSSN and KOMDIGI, brought together CISOs, policymakers, and solution providers to exchange strategies on zero trust, cloud security, and cyber resilience across banking, telecom, government, and other sectors.